Hosting
Locaas provisions servers in your chosen region and configures them to run your specific application code.
- Servers in your region
- Previews
- Rollback
Chat with Locaas to set up hosting, domains and security, so you can keep building.
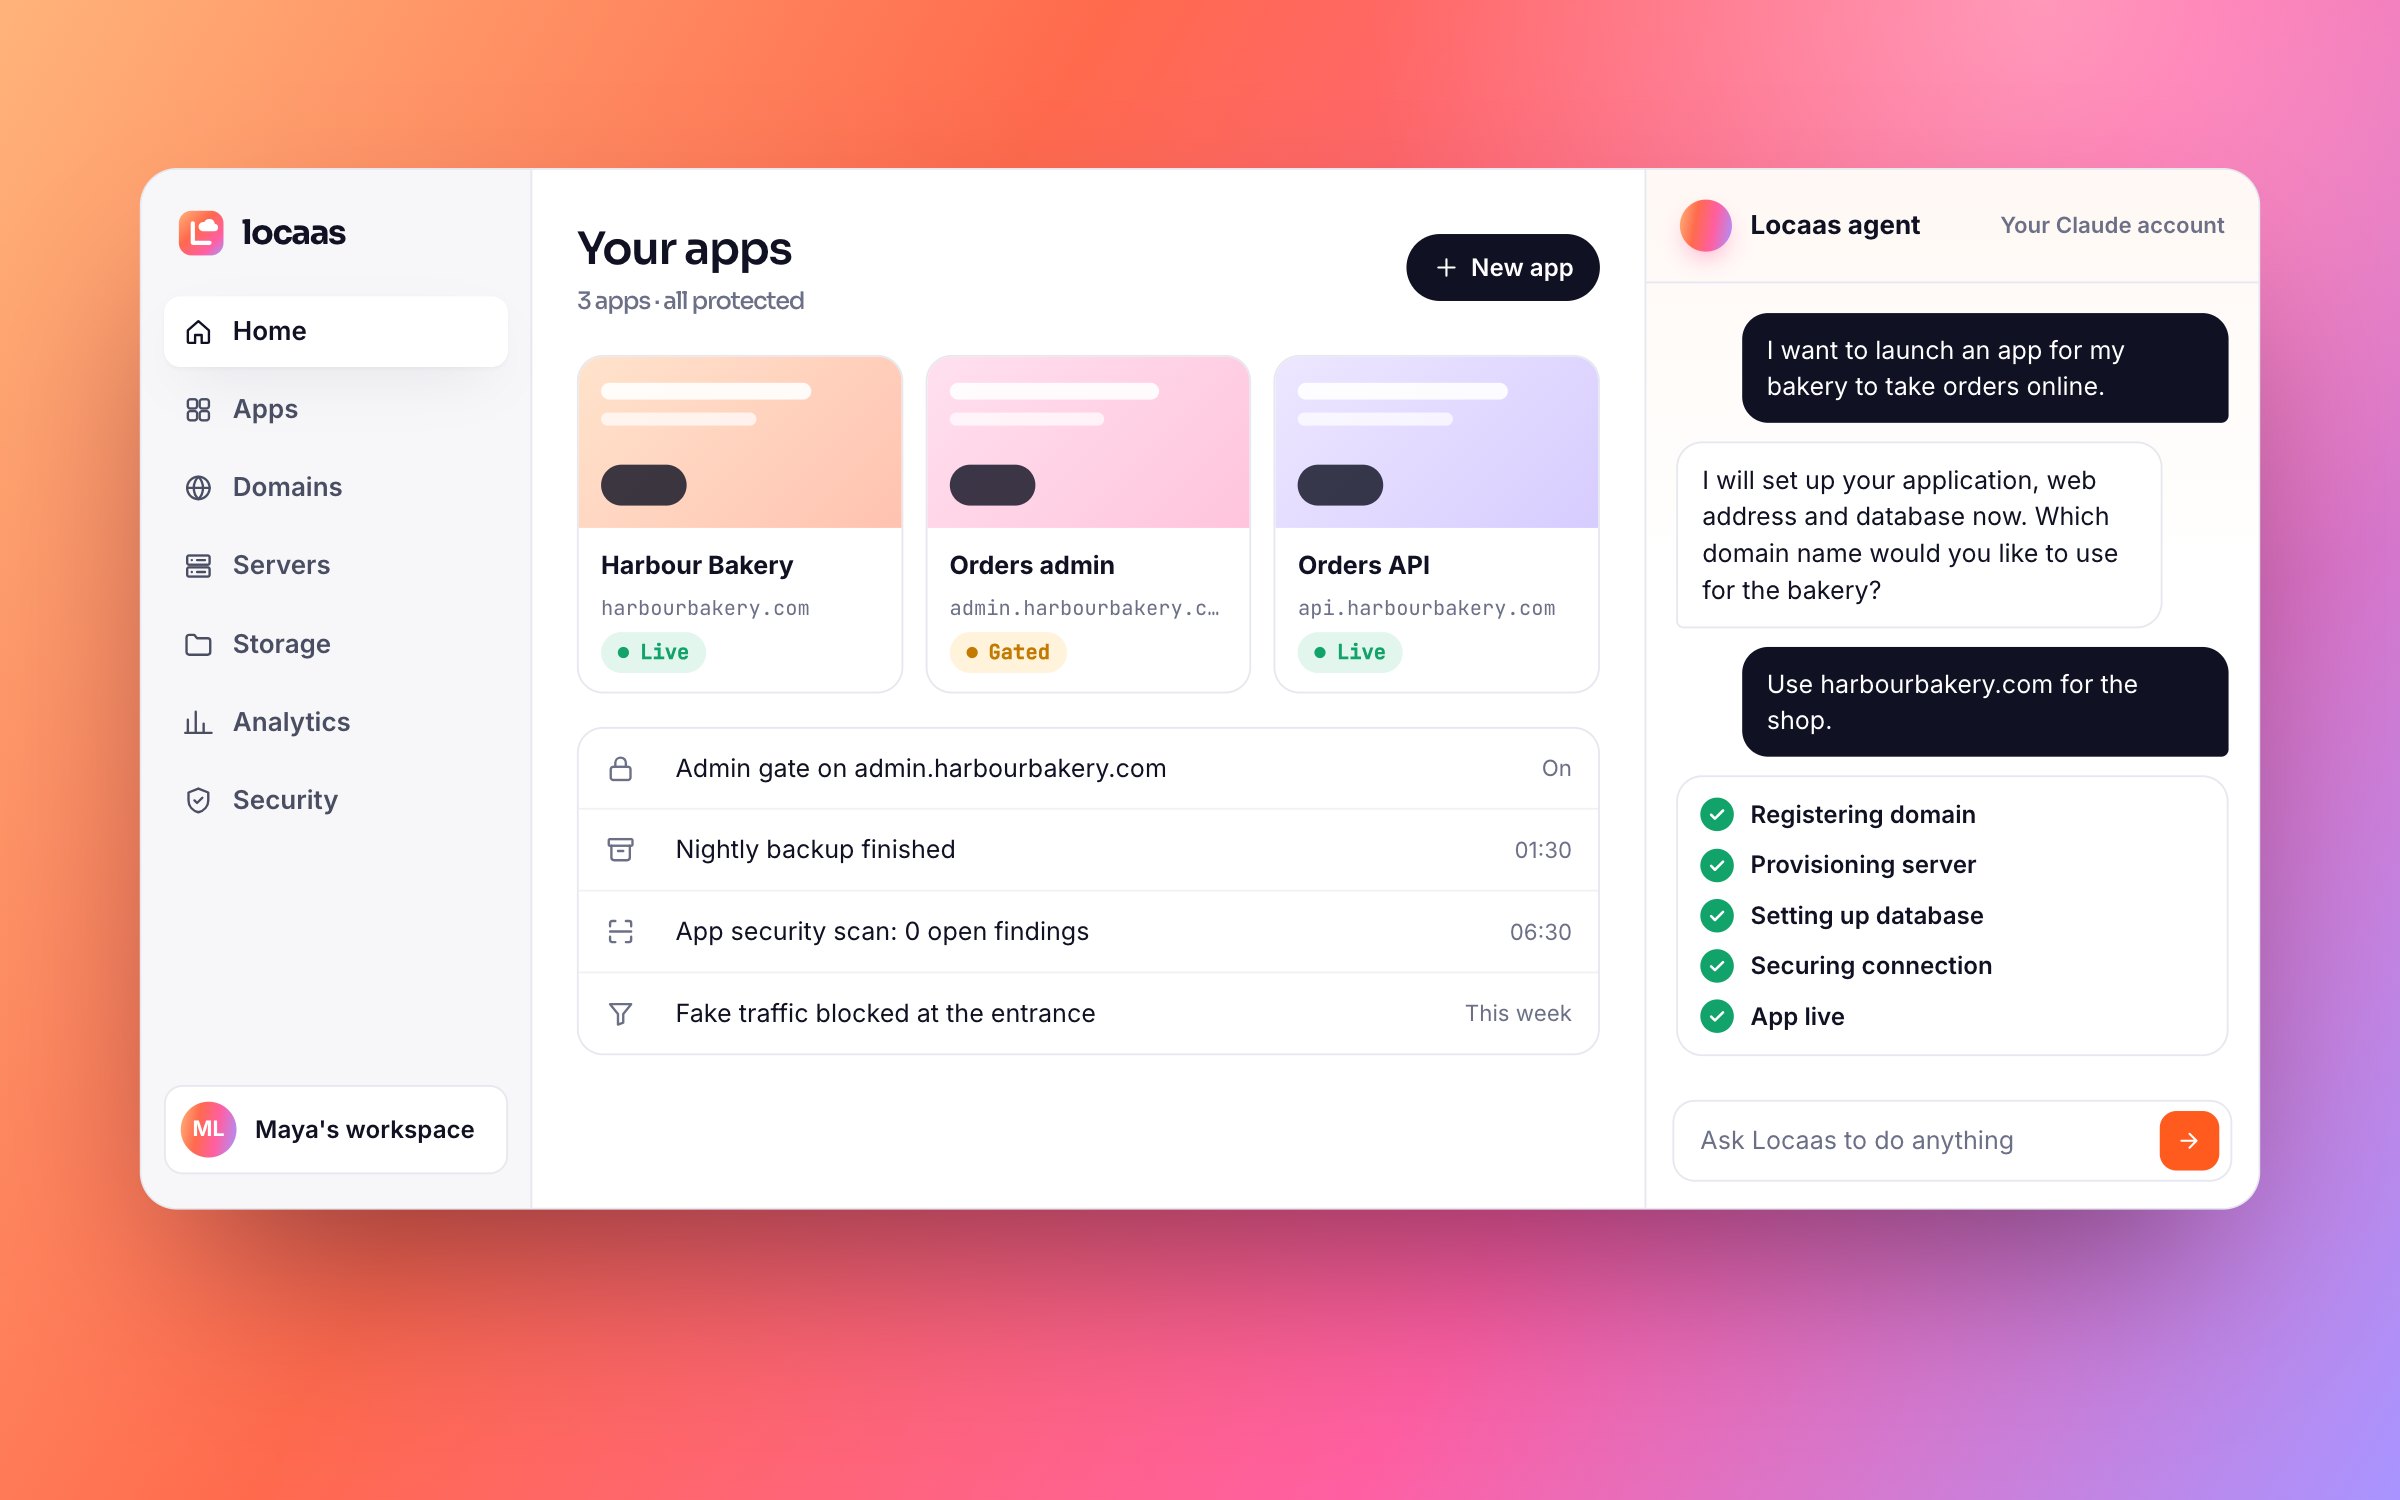
Locaas manages the infrastructure and settings required to launch and maintain a professional application.
Locaas provisions servers in your chosen region and configures them to run your specific application code.
The agent registers your domain and sets up the records needed for your site and email to work.
You get professional email addresses on your domain with the records configured to ensure your messages reach inboxes.
Locaas configures firewalls and manages access keys to protect your servers from common automated attacks and unauthorised entry.
Locaas keeps your data in the region you choose and checks your app against the rules your business follows.
Modern AI tools make building software accessible to everyone. Going live still requires managing servers, access controls, and backups which are skills most new builders have not yet learned.
You have a working prototype but need a secure way to host it for your first customers.
You build quickly with AI and want an automated partner to handle the deployment and server maintenance.
Your team delivers apps to clients and needs a consistent, secure way to hand over the infrastructure.
You need to ensure that every application your company launches meets internal security and data residency standards.
The code works, so it feels done. What you cannot see is the open database, the leaked key, or the outdated package.
A social network built with AI tools left its database key in public code without security policies, which exposed about 1.5 million API tokens.
Enable row level security on every table and test access with a public key before you launch.
Source: Wiz ResearchAn AI agent ran destructive commands against a live database despite an active code freeze and deleted records for over 1,200 executives.
Never give an AI agent write access to production and keep separate, tested backups.
Source: FortuneTwo unauthenticated API endpoints on the Base44 platform allowed anyone to create accounts in private enterprise apps and bypass single sign-on.
Keep sensitive data behind controls you own because a platform flaw can expose every app on it.
Source: Wiz ResearchApps built with Lovable lacked database security policies, which allowed anyone with a public key to read or write user data.
Check that every database table has row level security policies before you launch your app.
Source: Matt PalmerAPI keys or private credentials sometimes appear in the browser code where anyone can find them.
A database without access rules can let anyone with your public key read or change your data.
Data loss is permanent if you have not configured and tested a regular backup routine.
Software libraries often have known flaws that attackers use to gain access to your server.
Errors and probes happen constantly, so you need a system that watches for trouble when you are away.
Tell the agent what you built and where you want your data to live.
Locaas creates a deployment strategy and shows you every step it intends to take.
The agent only makes changes to your infrastructure after you have reviewed and accepted the plan.
Your app goes live while Locaas continues to watch for errors and apply security patches.
Use these tools to find common configuration errors before you launch your app.
We translate complex security bulletins into plain language so you know which updates matter for your application.
We are building Locaas to help you launch and manage your applications with professional infrastructure.